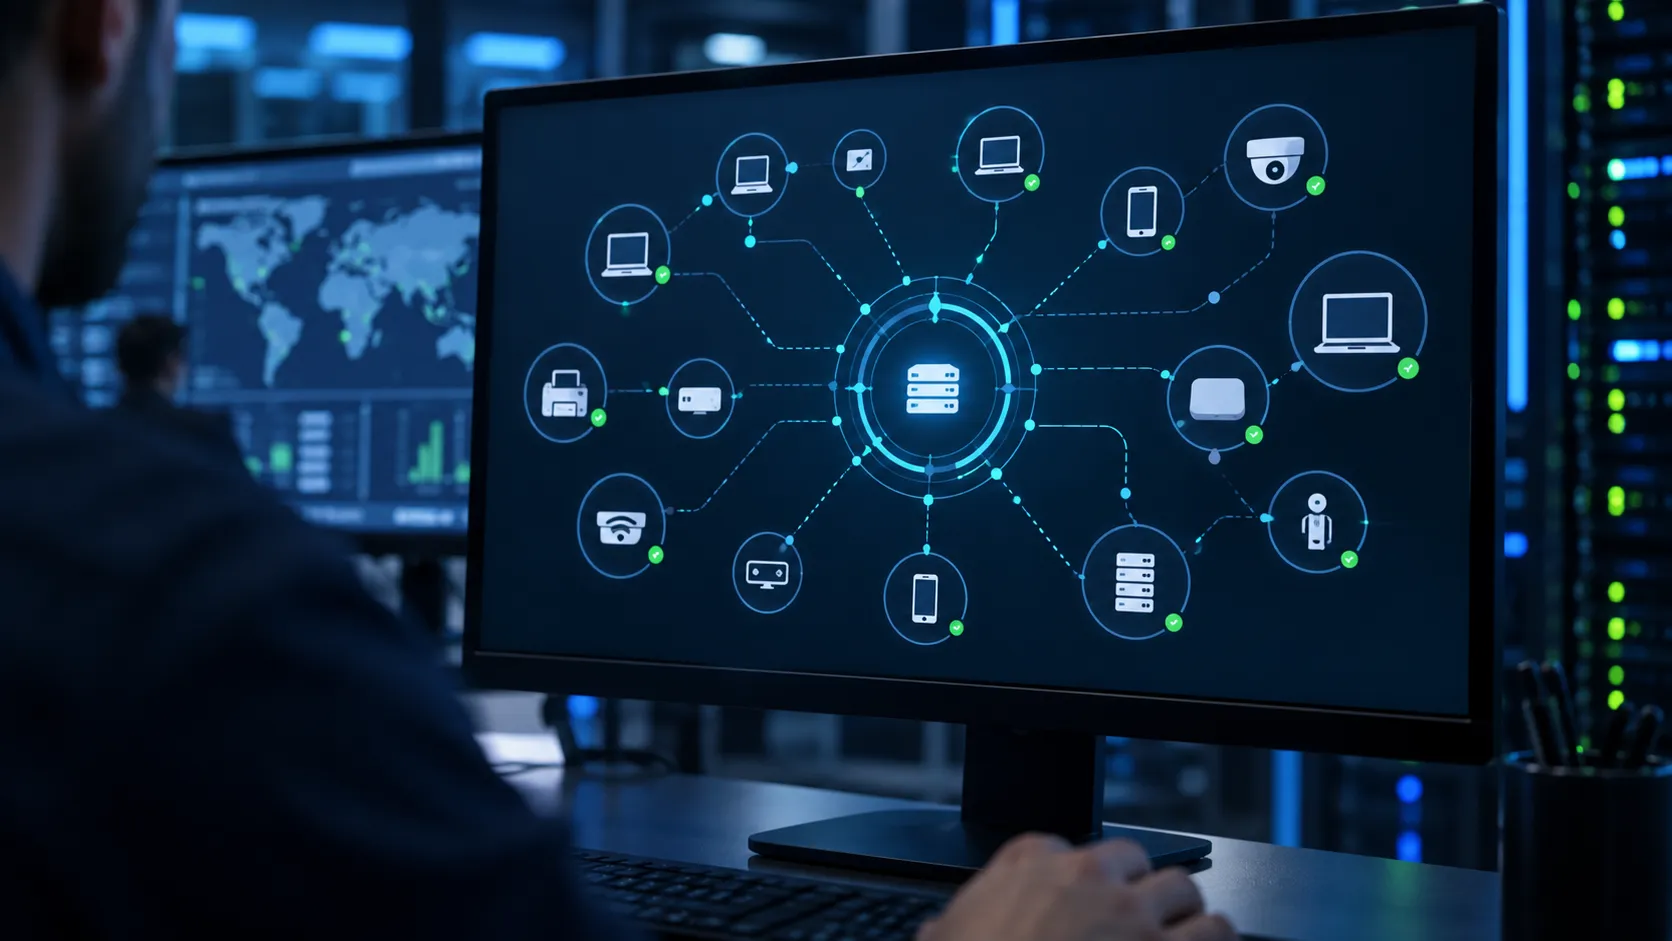
Network access control (NAC) is a security approach that identifies connected devices and users, checks them against access policies, and allows, restricts or blocks their network access.
NAC helps IT teams see corporate laptops, guest devices, printers, cameras and other connected equipment. It combines device discovery with identity and security information so that a network connection alone does not make a device trusted.
For example, EasyNAC can use Active Directory and supported XDR integrations to recognize managed devices, while blocking an unknown device according to policy. Agentless NAC can provide this visibility and control without deploying a dedicated NAC agent to every endpoint or requiring an 802.1X rollout.
How does network access control work?
A NAC deployment connects device discovery, assessment, policy and enforcement. The available information and enforcement methods depend on the network, endpoint capabilities and integrations. Access should be reassessed when a device's condition changes.
1. Discover connected devices
NAC builds an inventory from sources such as DHCP, ARP, switch and wireless information, and approved network scans. Visibility needs to cover the relevant wired networks, Wi-Fi and branch locations. Discovery alone does not prove a device is trusted; it establishes what needs to be assessed.
2. Assess identity and security posture
The system combines device profiles with available identity and security information. Certificates, directory records, ownership, endpoint protection or device management data can support a decision. A printer cannot provide the same evidence as a managed laptop. MAC addresses and device fingerprints are useful clues, but should not be treated as strong authentication by themselves.
3. Decide the appropriate access
Policies translate that evidence into access appropriate to the device and its role. A managed laptop might reach approved business services; a guest might receive internet access only; a camera might reach its recording server. Unknown devices can be restricted pending review. Exceptions need an owner and an expiry date.
4. Enforce and reassess
Depending on the architecture, NAC can use switch or wireless controls, VLANs, access control lists, firewall integrations or ARP-based enforcement. It can change access when posture fails or an integrated security tool raises an alert. Test both the initial decision and subsequent changes, including how access is restored after remediation.
NAC deployment examples: office, branches and security response
What does deploying network access control look like in practice? Follow these three EasyNAC examples to see how discovery, device trust and enforcement work together—from your first office to distributed sites and ongoing protection.
Why is NAC important? Benefits and use cases
A network connection should not automatically grant broad access to internal systems. NAC helps make access decisions consistent across devices that IT manages directly and equipment that cannot run endpoint security software.
- Rogue and unmanaged devices: identify unexpected equipment and apply a defined approval or restriction policy.
- Guest access and BYOD: give visitors, contractors and personal devices appropriate connectivity, separate from sensitive business resources.
- IoT and operational technology: profile devices such as cameras, printers and controllers, then limit access according to their function. Use discovery methods appropriate to fragile or safety-critical equipment.
- Incident response: use supported integrations with endpoint detection and response (EDR) or other security tools to restrict a device associated with a threat.
- Distributed sites: apply consistent policies and maintain visibility across offices and branches.
- Audit evidence: record device inventory, access decisions, exceptions and remediation. NAC can support a compliance program, but installing it does not establish compliance by itself.
Explore EasyNAC use cases for guest access and unmanaged devices for product-specific examples.
For distributed sites, explore Enforcer Sensors for branch protection and Central Visibility Manager for managing multiple EasyNAC appliances.
NAC approaches: agentless, agent-based and 802.1X
NAC solutions use different methods for device assessment and access control. Agentless discovery, endpoint agents and 802.1X address different parts of that process. EasyNAC provides agentless discovery, ARP-based enforcement and supported security integrations, and can work alongside existing 802.1X infrastructure.
Agentless network access control
Agentless NAC discovers and assesses devices without requiring a dedicated NAC agent on each endpoint. It uses network observations and supported integrations with identity, device management and security systems. This makes it useful for mixed environments containing IoT, OT, BYOD and guest equipment.
The main consideration is the evidence available for each device. Network profiling can identify likely device types, but detailed patch, encryption or endpoint protection checks may require credentials or an integration. Ask which checks are passive, which actively query endpoints, and which depend on another product. Agentless does not automatically mean every device or network path is covered.
See this in practice: Explore EasyNAC’s agentless NAC approach.
Agent-based assessment
A persistent or temporary endpoint agent can report local security information and help with remediation. This can be valuable for managed computers. Check operating system support, deployment effort and what happens to devices that cannot run the agent. Some environments combine agent-based posture checks with agentless discovery for the rest of the network.
802.1X-based network access control
IEEE 802.1X defines port-based network access control. In a common enterprise deployment, a device's supplicant communicates through a switch or access point with an authentication service. Certificate-based authentication can provide strong evidence of device or user identity.
An 802.1X deployment requires compatible infrastructure, endpoint configuration and policies for devices without supplicants. MAC authentication bypass is one possible exception mechanism, but a MAC address is easier to impersonate than a protected certificate. Assess the operational requirements rather than assuming 802.1X is always necessary or always unsuitable.
ARP-based enforcement
Some agentless solutions use Address Resolution Protocol (ARP) behavior to control IPv4 communication on a local network segment. This can support enforcement without requiring 802.1X on the access switch. Its suitability depends on network topology and the controls already in place. ARP is an IPv4 mechanism; evaluate IPv6 coverage separately, along with routed traffic, wireless isolation and switch security features.
Network access control for wired and wireless networks
NAC can assess devices and apply access policies on both Ethernet and Wi-Fi networks. The objective is consistent: identify the endpoint, evaluate the available security evidence and enforce the appropriate access. The connection type determines which discovery signals and enforcement controls are available.
- Wired NAC: evaluate how the solution discovers devices on switch ports and protected subnets. For EasyNAC, evaluate agentless discovery and ARP-based enforcement on the network segments you need to protect.
- Wireless NAC: evaluate corporate and guest Wi-Fi separately. EasyNAC can work alongside existing 802.1X authentication while providing agentless visibility and enforcement. Confirm how the NAC system sees individual clients and how restrictions reach them.
- Agentless coverage: test visibility and enforcement on each relevant subnet and SSID. Wireless client isolation, controller tunnelling and routed boundaries can affect which controls apply.
For example, test the same managed laptop on Ethernet and corporate Wi-Fi, then test a guest phone and a device that cannot run an agent. Verify discovery, the access decision, restriction after a failed check and restoration after remediation. A shared policy should produce the intended outcome on each connection type.
Pre-admission and post-admission NAC
Pre-admission control evaluates a connection before granting normal network access. Depending on the design, a device may have limited access to authentication, registration or remediation services while it is assessed.
Post-admission control reassesses connected devices and changes their access when risk or policy compliance changes. A complete evaluation should examine both the admission decision and the time between a later security event and effective containment. The two approaches can be used together.
NAC, firewalls, EDR and ZTNA: what is the difference?
- NAC: establishes device context and applies network access policy to connected users and endpoints.
- Firewalls: inspect and control traffic between hosts, zones or applications. Modern firewalls can also use identity and device context; NAC can supply additional information and enforcement requests.
- EDR: monitors supported endpoints for suspicious activity and supports investigation and response. NAC can extend a response to network access, including equipment without an EDR agent where supported.
- Zero Trust Network Access (ZTNA): brokers access to specific applications based on identity and context. It often serves remote and hybrid access needs, while NAC addresses access on the networks it controls.
These controls can work together. NAC is not a replacement for endpoint protection, application security, segmentation or recovery planning.
How NAC supports Zero Trust
NIST's Zero Trust Architecture rejects implicit trust based solely on network location or device ownership. NAC can contribute device information, access policy enforcement and reassessment. A broader Zero Trust design also considers users, applications, resources and sessions; deploying NAC alone does not complete that design.
See this in practice: See how EasyNAC automates threat response.
How to plan a NAC deployment
- Define scope: identify the sites, subnets, wireless networks, remote access paths and device groups to cover.
- Establish visibility: observe a representative environment and reconcile discovered devices with inventory and ownership records.
- Define policies and exceptions: specify evidence, allowed resources, remediation steps, owners and expiry dates.
- Pilot enforcement: test with a limited group, including unmanaged devices and critical services. Confirm that permitted work continues.
- Test failure and recovery: check behavior when a NAC component, integration or network link is unavailable, then document rollback and restoration.
- Roll out and review: expand in stages, review false classifications and exceptions, and measure operational results.
Deployment time depends on scope, existing infrastructure, integrations and policy readiness. Compare the effort to operate the solution after deployment as well as the initial installation.
Plan your deployment: Compare EasyNAC appliances and deployment options.
How to evaluate a network access control solution
Use a proof of concept with your own device mix. Ask each supplier to demonstrate the same tests:
- Coverage: which wired, wireless, branch, IPv4, IPv6 and remote access paths can it actually observe and control?
- Device assessment: which attributes are measured directly, inferred from profiling or obtained through integrations?
- Enforcement: can an unknown device be restricted, a known device isolated after an alert, and access restored safely?
- Compatibility: what switch, firewall, identity, EDR and device management dependencies apply?
- Resilience: what happens during component failure or lost connectivity, and which services remain reachable?
- Operations: can administrators explain a decision, manage an exception and export useful access records?
- Cost: account for licensing, appliances or sensors, integrations, support and ongoing administration.
Record measurable acceptance criteria such as inventory coverage, classification accuracy, containment time and administrator effort. Use observed results rather than a universal deployment-time promise.
Where EasyNAC fits
EasyNAC by InfoExpress provides agentless network access control for organizations that need visibility and enforcement across a mixed device estate. Its product range includes physical or virtual appliances, Enforcer Sensors for distributed locations, and centralized management. ARP-based enforcement and supported security integrations are part of its approach.
Review the EasyNAC appliances, sensors and management options, then use the deployment guides, technical whitepapers and demonstrations to assess the fit for your environment. A pilot should confirm your required topology, device checks, enforcement paths and integrations.
Contact EasyNAC to discuss your NAC requirements or arrange a demonstration.