Unapproved laptops and routers
Someone connects a personal device. Explore discovery, an Untrusted role and restricted corporate access.
Spot the risks. Connect EasyNAC. Put protection to the test.
Take charge of a fictional 500-device office. Discover what is connected, use the security tools you already have and see how network access control changes the outcome.
Free to explore. No sign-up. No changes to your network.
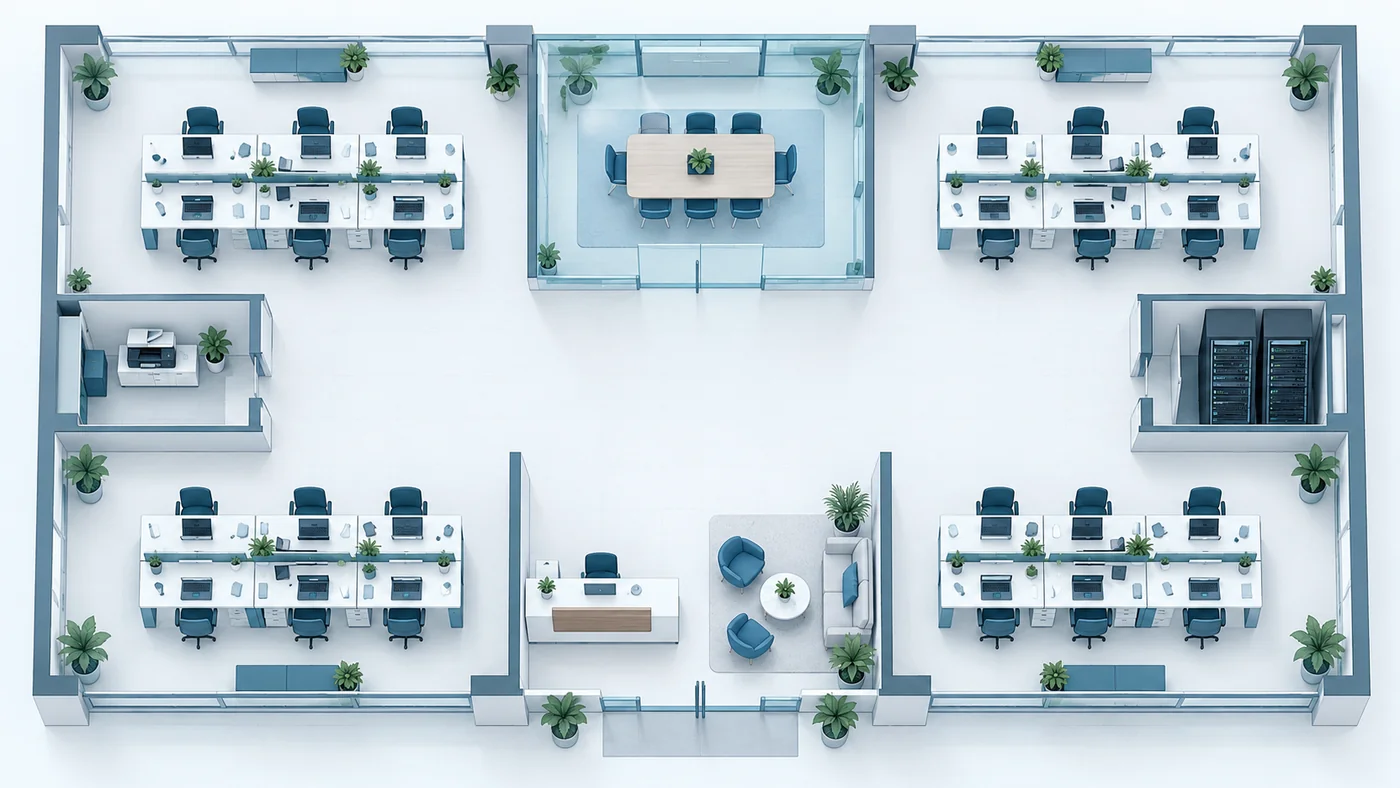
Click a risk in the experience to see its three-picture story. Then work through the controls that can help.
Someone connects a personal device. Explore discovery, an Untrusted role and restricted corporate access.
A managed laptop is no longer running XDR. Follow the remediation message, recovery and reassessment.
A visitor needs access. Follow a clear approval path while keeping corporate resources restricted.
Someone reuses a printer connection. Investigate a device identity conflict and the configured response.
A device is missing required patches. Use supported management evidence to drive an access decision.
An endpoint interacts with a decoy. See a simulated alert and configured source restriction.
Choose an appliance or VM, apply sample IP settings and watch devices appear in Device Manager.
Connect simulated AD, XDR and patch management. Review trust and health evidence, then confirm approved equipment.
Review the policy, enable enforcement and test unknown devices, remediation, guest approval and threat-response scenarios.
This prepared-network simulation illustrates configured access policies and supported integrations. It is not a deployment-time benchmark. Device management and health are evaluated separately; actual coverage and outcomes depend on your network design and policy.
Try EasyNAC and 802.1X side by side in the separate NAC Deployment Lab.
This is an interactive simulation using fictional devices and sample data. It does not scan your network or connect to your security tools. A real EasyNAC proof of concept validates coverage, integrations and access policies in your environment.
The scenario uses one EasyNAC physical or virtual appliance in a prepared 500-device office with existing Active Directory, XDR and patch management. You connect simulated sources, review device roles and enable enforcement.
Secure Your Office explains why NAC matters and lets you explore EasyNAC access controls. The NAC Deployment Lab compares the setup and maintenance work for EasyNAC and an 802.1X-based approach.
No. All actions and alerts inside the experience are simulated. The demo button opens our separate enquiry page, where you can choose to request a demonstration or discuss a proof of concept.
Bring your devices, network questions and security tools. Book a demo and plan your EasyNAC PoC.
Want the technical steps? Read the EasyNAC deployment guide.